Semiconductor Functional Safety & Security Across Safety-Critical Domains
Our semiconductor safety expertise spans automotive, industrial automation, energy and power electronics, medical devices, aerospace and defense, robotics and other safety-critical embedded applications. We support organizations from semiconductor safety planning and risk analysis through hardware safety architecture, failure analysis, safety mechanisms, verification, validation, safety documentation and assessment readiness.
Need support with an Semiconductor Functional Safety? Contact our Semiconductor Functional Safety experts
- Extreme semiconductor complexity: Modern SoCs and processors integrate CPU, GPU, AI accelerators, memories, peripherals, communication interfaces and safety mechanisms, making systematic safety analysis and verification demanding.
- Heterogeneous architectures: Safety-related and non-safety functions may share compute, memory, interconnect and peripherals, requiring careful partitioning and freedom-from-interference analysis.
- Random hardware failures: Semiconductor faults can arise from manufacturing defects, aging, wear-out, environmental stress, voltage/temperature conditions and other mechanisms.
- Soft errors and radiation effects: SEU/SET and other transient effects can affect memory, logic and state elements, particularly in demanding environments.
- Diagnostic coverage: Safety mechanisms must be selected and evaluated so that the device architecture can achieve the required safety metrics for the target application.
- Hardware/software interaction: Semiconductor safety depends on assumptions about system integration, software use, diagnostics, external monitoring and fault reaction.
- Safety across multiple markets: The same semiconductor IP may be integrated into automotive, industrial, medical, aerospace or robotics products with different safety standards and assurance expectations.
- Safety manual and integration assumptions: Device-level safety evidence is only useful when assumptions, constraints, failure rates, diagnostics and integration requirements are clearly communicated to customers.
- Security and safety convergence: Connected semiconductor devices increasingly require cybersecurity mechanisms whose failure or compromise may affect safety-related behavior.
- Time-to-market pressure: Safety analysis, FMEDA, documentation and verification can become schedule risks if introduced late in the semiconductor development lifecycle.
Need support with an Semiconductor Functional Safety? Contact our Semiconductor Functional Safety experts
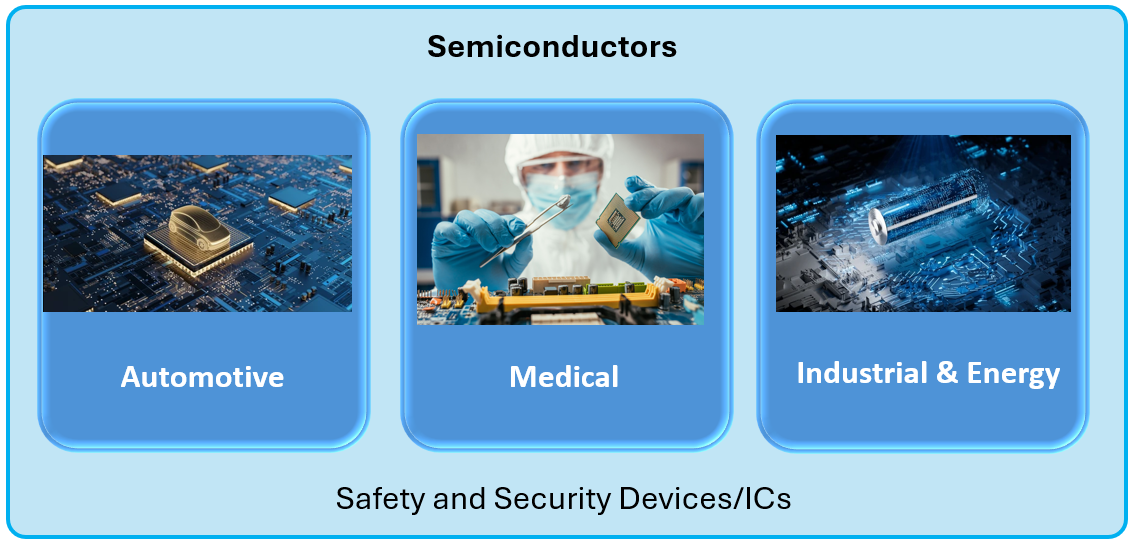
Automotive Semiconductors
- Microcontrollers (MCUs): Functional safety-enabled MCUs are used for engine control units (ECUs), ADAS, and autonomous driving systems.
- Sensors: Functional safety-certified sensors, such as LiDAR, radar, and cameras, for reliable environment sensing.
- Power Management ICs: Provide fail-safe power delivery in vehicles, including electric vehicle (EV) battery management systems.
- ASICs for Autonomous Vehicles: Custom chips designed with redundancy and fail-safe mechanisms for high-stakes operations.
- Wide Bandgap Semiconductors (SiC, GaN): Enable efficient and reliable power conversion in high-power safety-critical systems.
- Isolated Gate Drivers: Ensure electrical isolation and control in power electronics systems.
- Overcurrent and Overvoltage Protection ICs: Prevent damage in power delivery systems during faults.
Industry and Energy
- Programmable Logic Controllers (PLCs): Safety-compliant semiconductors in industrial controllers for automation.
- Safety-rated Sensors: Used in robotics and automation for detecting human presence and preventing accidents.
- Motor Control ICs: Ensure safe operation of industrial motors and actuators under varying conditions.
- Inverter Control ICs: Ensure safe conversion of DC to AC power in solar and wind energy systems.
- Grid-Tied Safety Chips: Support reliable connection of renewable energy sources to the power grid.
- Battery Management Systems (BMS): Semiconductors for managing and protecting energy storage systems in renewables
Medical Device Semiconductors
- Microcontrollers for Life Support Systems: Ensure reliability in ventilators, infusion pumps, and other life-critical devices.
- Implantable Device Chips: Low-power, fail-safe chips for pacemakers, cochlear implants, and drug delivery systems.
- Sensors for Diagnostic Equipment: Used in imaging devices like MRIs, CT scanners, and portable diagnostic tools.
- Communication ICs: Secure and reliable chips for wireless communication in wearable and implantable devices.
| Standard / Framework | Primary focus | Semiconductor relevance |
| ISO 26262 | Automotive functional safety | Semiconductor hardware/software development, safety mechanisms, hardware metrics and safety lifecycle for automotive applications |
| IEC 61508 | Functional safety of E/E/PE systems | Generic functional-safety foundation applicable to semiconductor components used in safety-related systems |
| ISO 13849 | Safety-related parts of control systems | Relevant to semiconductor devices used in machinery/control safety functions |
| DO-254 / ED-80 | Airborne electronic hardware | Relevant to semiconductor/FPGA/complex electronic hardware used in applicable airborne systems |
| ISO 21434 | Road-vehicle cybersecurity engineering | Relevant to automotive semiconductor cybersecurity and security assumptions where the device is part of a road-vehicle system |
| IEC 62443 | Industrial automation and control cybersecurity | Relevant to semiconductor devices used within industrial control and connected OT architectures |
| IEC 62304 | Medical-device software lifecycle | Relevant indirectly where semiconductor platforms support medical-device software; the device-level standard should be selected based on product scope |
| IEC 60601 | Medical electrical equipment safety | Relevant to semiconductor devices integrated into medical electrical equipment; system-level compliance remains application-specific |
| ISO 25119 | Safety-related parts of control systems for tractors/agricultural machinery | Relevant to semiconductor components used in applicable agricultural machinery safety functions |
| ISO 10218 / robotics standards | Robot safety | Relevant to semiconductor components used in safety-related robot control and protective functions |
The semiconductor device itself does not automatically become “compliant” with every downstream industry standard. The applicable safety standard, integrity level, development assurance and evidence depend on the intended use, safety context, device role and system integration.
Need support with an Semiconductor Functional Safety? Contact our Semiconductor Functional Safety experts
- Semiconductor-specific safety expertise: The current Semiconductor page positions VerveTronics around functional safety and device security for safety-critical semiconductor systems.
- Cross-domain safety knowledge: VerveTronics connects semiconductor safety with automotive, industrial, medical, aerospace/defense and robotics applications, helping translate device-level assumptions into system-level safety requirements.
- ISO 26262 and IEC 61508 experience: The existing Semiconductor page explicitly identifies these as core standards, while the broader site describes ISO 26262 up to ASIL D and IEC 61508 up to SIL3/SIL4 experience.
- Safety analysis capability: Existing content references FMEA and FTA and a semiconductor case involving ISO 26262 ASIL-D compliance from concept through assessment.
- People, Process, Tools and Continuous Improvement: The current Semiconductor page describes requirements engineering, traceability, CI/CD, HIL and fault-insertion testing, safety/security analysis and reusable accelerators.
- Safety + cybersecurity: VerveTronics explicitly combines functional safety with device cybersecurity, which is increasingly relevant to connected semiconductor platforms.
Need support with an Semiconductor Functional Safety? Contact our Semiconductor Functional Safety experts
Semiconductor Safety Concept & Planning
- Device safety scope and intended-use analysis
- Safety lifecycle planning
- Safety goals and safety requirements
- Safety architecture and partitioning
- Safety mechanism definition
- Safety manual structure and integration assumptions
- Safety plan and compliance matrix
- Safety case / evidence planning
Hardware Safety Analysis
- FMEA / FMEDA
- FTA / DFA
- Failure-mode classification
- Single-point and residual fault analysis
- Latent fault analysis
- Common-cause/dependent failure analysis
- Diagnostic coverage analysis
- SPFM / LFM / PMHF or applicable hardware safety metrics
- Failure-rate assumptions and FIT analysis
- Safety mechanism effectiveness analysis
Safety Architecture & Mechanisms
- Lockstep CPU architectures
- Safety islands
- Redundancy and diversity
- ECC memory
- Watchdogs
- Clock and voltage monitoring
- Temperature monitoring
- CRC and end-to-end protection
- Built-in self-test
- Memory and logic diagnostics
- Fault containment and safe-state support
- Freedom-from-interference mechanisms
Software & Hardware Interface Safety
- Hardware/software interface requirements
- Safety-related drivers and diagnostics
- Startup and initialization safety
- Fault reporting and reaction
- Diagnostic software interaction
- Safety mechanism configuration
- Safety-related register and memory protection
- Traceability from system assumptions to device implementation
Verification & Validation
- Safety mechanism verification
- Fault injection
- Hardware-in-the-loop testing
- Simulation and emulation
- Diagnostic coverage validation
- Random-fault testing
- Safety requirement verification
- Regression testing
- Failure-response timing verification
- Verification evidence review
Semiconductor Cybersecurity
- Threat analysis and risk assessment
- Security architecture
- Secure boot
- Hardware root of trust
- Cryptographic acceleration
- Key management interfaces
- Debug/access protection
- Secure update mechanisms
- Security monitoring
- Safety-security interface analysis
Safety Assessment & Certification Support
- Gap assessment against applicable standard
- Safety documentation review
- Safety manual review
- Customer safety-integration support
- Assessment evidence preparation
- Independent technical review
- Safety case support
- Certification-readiness support
Training & Consulting
- ISO 26262 semiconductor workshops
- IEC 61508 semiconductor workshops
- FMEDA and hardware metrics training
- Safety mechanism architecture reviews
- Safety manual development workshops
- Semiconductor cybersecurity workshops
Need support with an Semiconductor Functional Safety? Contact our Semiconductor Functional Safety experts
 For an Global Semiconductor IP leader we were part of global team to setup best practices and assisting projects in safety compliance as per ISO 26262 ASIL-D from concept to assessment for Automotive Segment.
VerveTronics Role:
- Support for end to end ISO 26262 ASIL-D compliance and assessment
- Safety/Technical Concept and specifications ,
- Safety Analysis for System (HARA), Hardware(FMEDA), Software(FMEA)
- Safety Compliant Hardware Specifications and Assessment
- Hardware Design and development
- Safety Compliant Software Specifications, Validation and Assessment
- ASIL-D / SIL3 Process Development and Improvements
- Safety Assessment and Certifications
 We successfully contributed in development of Safety Compliant TCP IP/Ethernet core for a leading Semiconductor company according to ASIL-D rating
VerveTronics Role:
- Support for end to end ISO 26262 ASIL-C compliance
- Safety/Technical Concept and specifications ,
- Safety Analysis for Hardware(FMEDA), Software (FMEA) and Mechanical (FMEA)
- Safety Compliant Hardware Specifications and Assessment
- Safety Compliant Software Specifications and Assessment
- ASIL-C / ASPICE Process Development and Improvements
- Safety Assessment
 We worked with a leading Semiconductor IC manufacturer to develop Imaging Sensor according to ASIL-B rating
VerveTronics Role:
- Safety/Technical Concept and specifications ,
- Safety Analysis for Hardware(FMEDA), Software (FMEA) and Mechanical (FMEA)
- Safety Compliant Hardware Specifications and Assessment
- Safety Compliant Software Specifications and Assessment
- Safety Assessment.
- Perform safety and threat analysis with clear ownership of safety and security objectives.
- Identify interfaces where cybersecurity compromise could affect safety assumptions.
- Protect debug, test and manufacturing interfaces according to product requirements.
- Define secure boot and update strategies where applicable.
- Protect safety configuration and diagnostic mechanisms from unauthorized modification.
- Consider fault injection from both accidental and malicious perspectives where appropriate.
- Maintain traceability between safety assumptions, security controls and system integration requirements.
- Provide clear safety/security assumptions to downstream customers integrating the semiconductor into their products.
Need support with an Semiconductor Functional Safety? Contact our Semiconductor Functional Safety experts
Engagement Models
- Semiconductor safety work package – FMEDA, FMEA, FTA, DFA, safety metrics or safety mechanism analysis.
- Dedicated semiconductor safety engineering team – lifecycle support from concept through assessment.
- Expert consulting – architecture, safety mechanisms, hardware metrics and safety documentation.
- Safety manual / integration support – device assumptions, constraints, diagnostics and customer integration guidance.
- Assessment readiness – gap analysis, evidence review and corrective-action support.
- Safety + cybersecurity work package – coordinated safety/security architecture and analysis.
- Training and workshops – ISO 26262, IEC 61508, FMEDA, safety metrics and semiconductor security.
Developing a safety-critical semiconductor, MCU, SoC, FPGA or power-management IC?
Talk to VerveTronics about functional safety, hardware safety metrics, safety mechanisms and device cybersecurity.
Need an ISO 26262 / IEC 61508 semiconductor safety assessment or FMEDA review?
Share your device architecture, intended applications and target integrity level for an initial technical discussion.
Need support with an Semiconductor Functional Safety? Contact our Semiconductor Functional Safety experts
- What is semiconductor functional safety? – Semiconductor functional safety is the engineering discipline used to reduce risks arising from semiconductor hardware and its associated software/interfaces when the device is integrated into a safety-related system.
- Why is functional safety important for semiconductor devices? – A semiconductor device may perform safety-related processing, sensing, communication, power management or diagnostics. Failures can therefore contribute to hazardous system behavior unless detected, controlled or otherwise mitigated.
- Which functional safety standards apply to semiconductors? – The applicable standard depends on the intended application. Common frameworks include ISO 26262 for automotive, IEC 61508 for generic E/E/PE functional safety, ISO 13849 for machinery control applications, DO-254 for applicable airborne electronic hardware and other sector-specific standards.
- What is ISO 26262 semiconductor safety? – It is the application of ISO 26262 hardware/software development and safety principles to semiconductor devices used in road-vehicle systems, including analysis of random hardware failures, safety mechanisms, metrics and integration assumptions.
- What is IEC 61508 semiconductor safety? – IEC 61508 provides a generic functional-safety framework that can be relevant to semiconductor devices used as components in safety-related electrical, electronic and programmable electronic systems.
- Can VerveTronics support ASIL-D semiconductor projects? – VerveTronics supports global semiconductor IP projects with ISO 26262 ASIL-D safety compliance from concept through assessment.
- Can VerveTronics perform semiconductor FMEDA? – Yes. FMEDA is explicitly included in the semiconductor-oriented service positioning and in VerveTronics’ broader functional safety analysis capability.
- What semiconductor safety mechanisms are commonly considered? – Depending on architecture, examples include lockstep processing, ECC, watchdogs, clock/voltage/temperature monitoring, built-in self-test, CRC/end-to-end protection, redundancy and fault containment.
- What are SPFM, LFM and PMHF? – They are hardware safety metrics used in applicable ISO 26262 analyses to characterize different categories of random hardware failure risk. Their applicability and calculation depend on the product architecture, safety goal and ISO 26262 context.
- How do SEU and SET affect semiconductor safety? – Single-event upsets and single-event transients can cause temporary or persistent changes in semiconductor state or signals. Their significance depends on the application environment, device technology, architecture and required safety behavior.
- Can semiconductor safety and cybersecurity be combined? – Yes. They should remain distinct engineering disciplines with coordinated interfaces. Security threats can affect safety assumptions, especially in connected or updateable devices.
- Can VerveTronics support semiconductor safety manuals? – Yes. Safety documentation and integration assumptions can be addressed as part of a semiconductor safety engineering work package, including customer-facing assumptions, constraints and diagnostic information.
- Can VerveTronics support industrial and energy semiconductors? – The VerveTronics semiconductor expertise across industrial and energy-related applications, while the broader Industrial domain covers power/energy storage, controls, sensors and connectivity.
- Can semiconductor safety be applied to medical and aerospace products? – Yes, but the applicable system-level standards and assurance framework must be established for the intended product. The semiconductor should be analyzed in the context of its role and integration into the end system.
- When should semiconductor safety engineering start? – It should begin early, ideally during device architecture and product planning, because safety mechanisms, redundancy, diagnostics, area/power/performance tradeoffs and documentation assumptions can materially affect the silicon architecture.
Automotive safety MCUs and SoCs
Radar, sensor-interface and perception-support ICs