Defense & Airborne Functional Safety | DO-178C, DO-254 & Avionics
Our expertise covers DO-178C software development assurance and DO-254 airborne electronic hardware development assurance, supported by system safety analysis, hardware/software engineering, verification and validation, safety assessment and certification readiness.
The page should serve as the Defense & Airborne domain hub while specialist pages capture high-intent searches for DO-178C, DO-254, controls/navigation/connectivity, power/electrical systems, sensors/surveillance and Airborne safety ICs.
Need support with an Defense & Airborne Functional Safety? Contact our Defense & Airborne Functional Safety experts
- Safety-critical avionics complexity: Flight controls, navigation, communication, radar, power and mission systems increasingly combine software, FPGA/programmable hardware and networked electronics.
- High development-assurance rigor: DO-178C and DO-254 require disciplined lifecycle processes, defined objectives, evidence and traceability appropriate to the applicable assurance level.
- Hardware/software interaction: Airborne systems require consistent allocation and traceability between system requirements, software requirements, hardware requirements and implementation.
- Certification evidence burden: Planning, reviews, verification results, configuration management, problem reports, traceability and compliance evidence must remain consistent throughout the lifecycle.
- Complex airborne hardware: FPGA, ASIC, COTS devices and other complex electronic hardware can introduce verification, configuration and assurance challenges.
- Real-time and deterministic behavior: Flight-control, navigation, communication and mission functions depend on predictable timing, fault handling and robust interfaces.
- Sensor and navigation dependence: GNSS, inertial, radar and environmental sensors influence flight decisions and require appropriate failure detection, redundancy and degraded-mode behavior.
- Power integrity: Aircraft and UAV power distribution and conversion failures can propagate into multiple safety-critical loads.
- Connected and autonomous platforms: UAVs, autonomous flight systems and connected avionics increase the interaction between safety, security, communications and operational behavior.
- Certification schedule pressure: Late safety-process gaps or missing objective evidence can create costly rework and certification delays.
Need support with an Defense & Airborne Functional Safety? Contact our Defense & Airborne Functional Safety experts
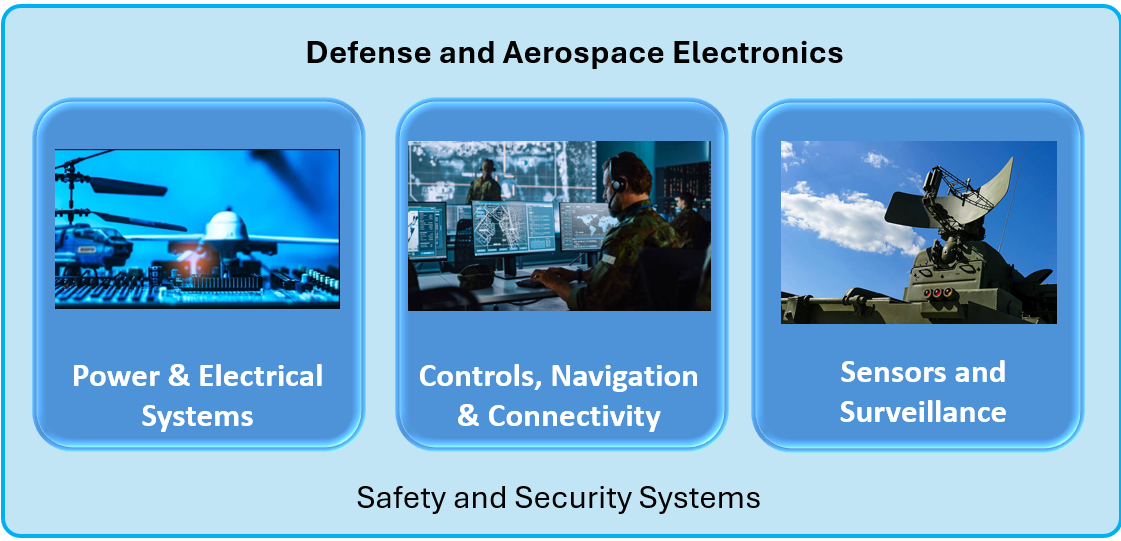
Power and Electrical Systems
- Power Distribution Units (PDUs): Intelligent systems that safely manage power supply to avionics and mission-critical equipment.
- High Power DC-DC converters: High power DC-DC converters to manage varied and high load requirements
- Energy Storage and Batteries: Safety features to prevent thermal runaway or overcharging.
- Fault-Tolerant Power Supplies: Redundant systems to maintain uninterrupted power for critical functions.
- Power Generation and Distribution: Reliable and safe systems for powering ground-based support equipment
Controls, Commands and Navigation
- Communication Systems: Secure and interference-resistant communication between aircraft and ground control.
- Inertial Navigation Systems (INS): Redundancy to ensure navigation accuracy in GPS-denied environments.
- Fly-by-Wire Systems: Electronically controlled flight systems replacing mechanical linkages, ensuring redundancy and fail-safe mechanisms.
- Guided Missile Electronics: Safety protocols to prevent unintentional launches or detonation.
- Military Vehicles: Electronic control units (ECUs) with fail-safe and redundancy for navigation, powertrain, and defense systems.
- Autonomous Combat Systems: Safety mechanisms for autonomous ground and air combat systems
Sensors and Surveillance
- Sensor Integration: Redundant sensors for altitude, speed, and attitude measurements to prevent critical failures.
- Radar Systems: Fail-safe operation to ensure uninterrupted tracking and targeting capabilities.
- Electro-Optical/Infrared Systems (EO/IR): Redundant electronics for reliable imaging in adverse conditions.
- Weapon Guidance Systems: Functional safety measures to ensure accurate and secure operation.
- Electronic Warfare (EW) Systems: Fail-safe mechanisms to handle signal jamming and electronic countermeasures.
- Avionics Test Equipment: Safety in testing and maintaining avionics systems.
- Launch and Recovery Systems: Electronics for safe handling of aircraft or UAV takeoff and landing.
| Standard / Framework | Primary focus | Typical relevance |
| DO-178C / ED-12C | Airborne software development assurance | Safety-critical airborne software lifecycle, verification and evidence |
| DO-254 / ED-80 | Airborne electronic hardware development assurance | Complex/custom airborne electronic hardware, including FPGA/ASIC-related development |
| ARP4754A | Guidelines for development of civil aircraft and systems | System development process and requirements allocation |
| ARP4761 / ARP4761A* | Safety assessment process | Aircraft/system safety assessment activities where applicable |
| DO-160 | Environmental conditions and test procedures for airborne equipment | Environmental qualification/testing |
| DO-330 | Software tool qualification | Tool qualification where tool outputs are used in certification-relevant activities |
| DO-331 | Model-Based Development and Verification | Model-based software development/verification supplement |
| DO-332 | Object-Oriented Technology and Related Techniques | Applicable software techniques supplement |
| DO-333 | Formal Methods | Formal-methods supplement for applicable software assurance activities |
| DO-297 | Integrated Modular Avionics | IMA development and certification considerations |
| Cybersecurity framework – project specific | Airborne/defense cybersecurity | Security engineering according to applicable regulatory, program and customer requirements |
*Use the specific applicable revision and regulatory basis for the project. The page should not imply that every listed standard applies to every defense/Airborne program.
FAA guidance currently recognizes DO-178C/ED-12C through AC 20-115D for software and DO-254/ED-80 through AC 20-152A for airborne electronic hardware as acceptable means of compliance in the applicable certification context
Need support with an Defense & Airborne Functional Safety? Contact our Defense & Airborne Functional Safety experts
- Existing Airborne/defense experience: The current VerveTronics page describes expertise in safety-critical avionics for defense and Airborne platforms, including hardware, FPGA, firmware, electrical and software solutions for airborne systems and UAVs.
- End-to-end DO-178C/DO-254 support: Current case studies describe support from safety/technical concept and specifications through hardware/software assessment, process improvement and certification support.
- Cross-domain engineering: The existing page covers power/electrical systems, controls, navigation, connectivity, sensors, radar and autonomous systems.
- Safety analysis capability: Existing material explicitly references FMEA, FMEDA and FTA across system, hardware, software and mechanical aspects.
- Verification and validation: Existing VerveTronics content highlights requirement-based testing, structural coverage, integration testing and IV&V.
- Certification-support positioning: The website should distinguish engineering/compliance/certification support from the formal approval decision made by the applicable certification authority or designated organization.
Need support with an Defense & Airborne Functional Safety? Contact our Defense & Airborne Functional Safety experts
DO-178C Airborne Software Safety
- Software planning and lifecycle tailoring
- Software requirements engineering
- High-level and low-level requirements
- Software architecture and design
- Requirements traceability
- Software verification and validation
- Requirements-based testing
- Structural coverage analysis including MC/DC where applicable
- Integration and system testing
- Configuration and quality assurance support
- DO-178C compliance evidence and certification support
DO-254 Airborne Electronic Hardware
- Hardware planning and lifecycle definition
- Hardware requirements and architecture
- Detailed design and implementation support
- FPGA/PLD/ASIC development assurance
- Hardware verification and validation
- COTS/IP assessment considerations
- Hardware/software interface analysis
- Failure analysis and safety mechanisms
- DO-254 evidence and compliance support
- Certification readiness and assessment support
System Safety & Certification Engineering
- Functional hazard analysis / system hazard analysis
- Safety requirements allocation
- FMEA / FMEDA / FTA
- Fault detection and fault reaction
- Redundancy and fail-safe architecture
- Safety assessment support
- Requirements traceability and evidence review
- Certification plans and compliance matrices
Controls, Navigation & Connectivity
- Flight-control safety engineering
- Navigation and guidance safety
- Radar system safety analysis
- Telemetry and command interfaces
- Communication architecture safety
- Interface failure analysis
- Data integrity and loss-of-communication behavior
Power & Electrical Safety
- PMU/PDU safety analysis
- Power converter safety
- Protection and fault handling
- Power-domain independence analysis
- Thermal and electrical failure analysis
- Energy storage and battery interfaces
Sensors & Surveillance
- Sensor failure-mode analysis
- Sensor diagnostics and monitoring
- Redundancy and voting concepts
- Radar/surveillance safety analysis
- Navigation sensor fault handling
- Environmental and operational failure considerations
Verification, Validation & IV&V
- Verification planning
- Requirement-based test strategy
- Structural coverage strategy
- Hardware verification
- Software integration testing
- System validation
- Fault injection and robustness testing strategy
- Independent reviews and IV&V support
Process, Training & Consulting
- DO-178C/DO-254 process gap assessment
- Development process definition and improvement
- Tool-chain and workflow assessment
- Engineering team training
- Certification readiness workshops
- Independent technical reviews
Need support with an Defense & Airborne Functional Safety? Contact our Defense & Airborne Functional Safety experts
 We worked with European OEM for Electronics Power Management Unit as per DO-178C/ DO 254 for end to end concept to certification support for UAV system.
VerveTronics Role:
- Support for end to end DO-178C/ DO-254 compliance and certification
- Safety/Technical Concept and specifications ,
- Safety Analysis for System (HARA), Hardware(FMEDA), Software(FMEA) and Mechanical (FMEA)
- Safety Compliant Hardware Specifications and Assessment
- Hardware Design and development
- Safety Compliant Software Specifications, Validation and Assessment
- DO-178C/ DO-254 Process Development and Improvements
- Safety Assessment and Certifications
 We successfully contributed in development for a leading Tier-1 supplier of RADAR System according to DO-178C/ DO-254
VerveTronics Role:
- Support for end to end DO-178C/ DO-254 compliance
- Safety/Technical Concept and specifications ,
- Safety Analysis for Hardware(FMEDA), Software (FMEA) and Mechanical (FMEA)
- Safety Compliant Hardware Specifications and Assessment
- Safety Compliant Software Specifications and Assessment
- DO-178C/ DO-254 Process Development and Improvements
- Safety Assessment
 We worked with a leading Tier-1 supplier to develop Airborne Equipment Fire and Control System according to DO-178C/ DO-254
VerveTronics Role:
- Safety/Technical Concept and specifications ,
- Safety Analysis for Hardware(FMEDA), Software (FMEA) and Mechanical (FMEA)
- Safety Compliant Hardware Specifications and Assessment
- Safety Compliant Software Specifications and Assessment
- Safety Assessment.
- Identify interfaces where a security compromise could affect safety-related behavior.
- Define safe behavior for communication loss, corrupted data, invalid commands and degraded navigation/sensor inputs.
- Protect configuration, software and hardware update mechanisms according to the applicable program security requirements.
- Consider access control, secure communications, network segmentation and integrity protection for connected systems where applicable.
- Maintain clear allocation between safety objectives, security objectives and certification evidence.
- Evaluate emerging autonomous-system behaviors and human-machine interactions for both safety and security consequences.
VerveTronics explicitly as experts in positions controls, navigation and connectivity as areas where safety and cybersecurity intersect
Need support with an Defense & Airborne Functional Safety? Contact our Defense & Airborne Functional Safety experts
Engagement Models
- DO-178C work package – software planning, requirements, verification, testing, coverage or evidence.
- DO-254 work package – hardware planning, requirements, architecture, FPGA/complex hardware verification or compliance evidence.
- End-to-end safety engineering – system safety through hardware/software implementation and assessment readiness.
- Independent technical review / IV&V – targeted review of requirements, architecture, analyses, tests and evidence.
- Process gap assessment – identify missing or inconsistent lifecycle objectives before formal assessment.
- Training and workshops – DO-178C, DO-254, safety analysis, V&V and certification-readiness topics.
Developing safety-critical Airborne or defense electronics?
Talk to VerveTronics about DO-178C, DO-254, avionics safety, UAV systems, power electronics, controls, navigation, sensors or connectivity.
Need a DO-178C / DO-254 gap assessment or certification-readiness review?
Share your system architecture, target assurance level and development lifecycle for an initial technical discussion.
Need support with an Defense & Airborne Functional Safety? Contact our Defense & Airborne Functional Safety experts
- What is DO-178C? – DO-178C is guidance for software considerations in airborne systems and equipment certification. FAA AC 20-115D recognizes DO-178C/ED-12C as an acceptable means of compliance in the applicable certification context.
- What is DO-254? – DO-254 is design assurance guidance for airborne electronic hardware. FAA AC 20-152A recognizes ED-80/DO-254 and provides additional guidance for applicable airborne electronic hardware certification activities.
- What is the difference between DO-178C and DO-254? – DO-178C addresses airborne software development assurance, while DO-254 addresses airborne electronic hardware development assurance. They address different development domains and are often coordinated at system and hardware/software interface levels.
- What are DAL A through E? – Design Assurance Levels indicate the level of development assurance rigor associated with the consequences of failure in the applicable airborne system context. The applicable level is established through the system safety and certification process.
- Does DO-254 apply to FPGA development? – DO-254 can apply to airborne electronic hardware containing complex devices such as FPGA/PLD technology. The exact applicability and objectives depend on the hardware architecture and certification basis. FAA AC 20-152A provides relevant guidance.
- Can VerveTronics support DO-178C software verification? – Yes. Existing VerveTronics content describes requirements-based testing, structural coverage analysis, integration testing and IV&V support for safety-critical software.
- Can VerveTronics support DO-254 hardware verification? – Yes. Existing Airborne content describes hardware specifications, assessment, hardware design/development and DO-254 compliance/certification support.
- Can VerveTronics support UAV safety? – Yes. The current site specifically describes UAV work, including an Electronics Power Management Unit project developed according to DO-178C/DO-254.
- Can VerveTronics support radar safety? – The current site states that VerveTronics contributed to a Tier-1 RADAR system development according to DO-178C/DO-254, including hardware/software safety analysis and assessment activities.
- Can VerveTronics support Airborne power electronics? – Yes. The current Defense & Airborne page identifies power distribution and Power Management Unit expertise and includes an Airborne power-management case study.
- Can VerveTronics support navigation and connectivity systems? – Yes. The current site has a dedicated Controls, Navigation & Connectivity Defense page covering controls, navigation and connectivity as safety/security-relevant system domains.
- What other standards may interact with DO-178C and DO-254? – Depending on the program, related frameworks can include ARP4754A, ARP4761/ARP4761A, DO-160, DO-297 and the DO-330/331/332/333 supplements. The exact certification basis must be established for the project.
- Does VerveTronics provide formal aircraft certification? – The website should position VerveTronics as providing engineering, compliance and certification-support services. Formal regulatory approval or independent certification remains subject to the applicable authority, designated organization and certification process.
- When should DO-178C/DO-254 activities begin? – They should be incorporated early in the system development lifecycle so planning, requirements, architecture, verification strategy, configuration management and evidence expectations influence the design from the beginning.
- Can safety and cybersecurity be addressed together? – Yes, at the system-engineering level. Safety and cybersecurity have different objectives, but threat consequences can interact with safety-related functions, particularly in connected, autonomous and mission-critical platforms.